Security standards at Tidely
Security and data protection
you can rely on
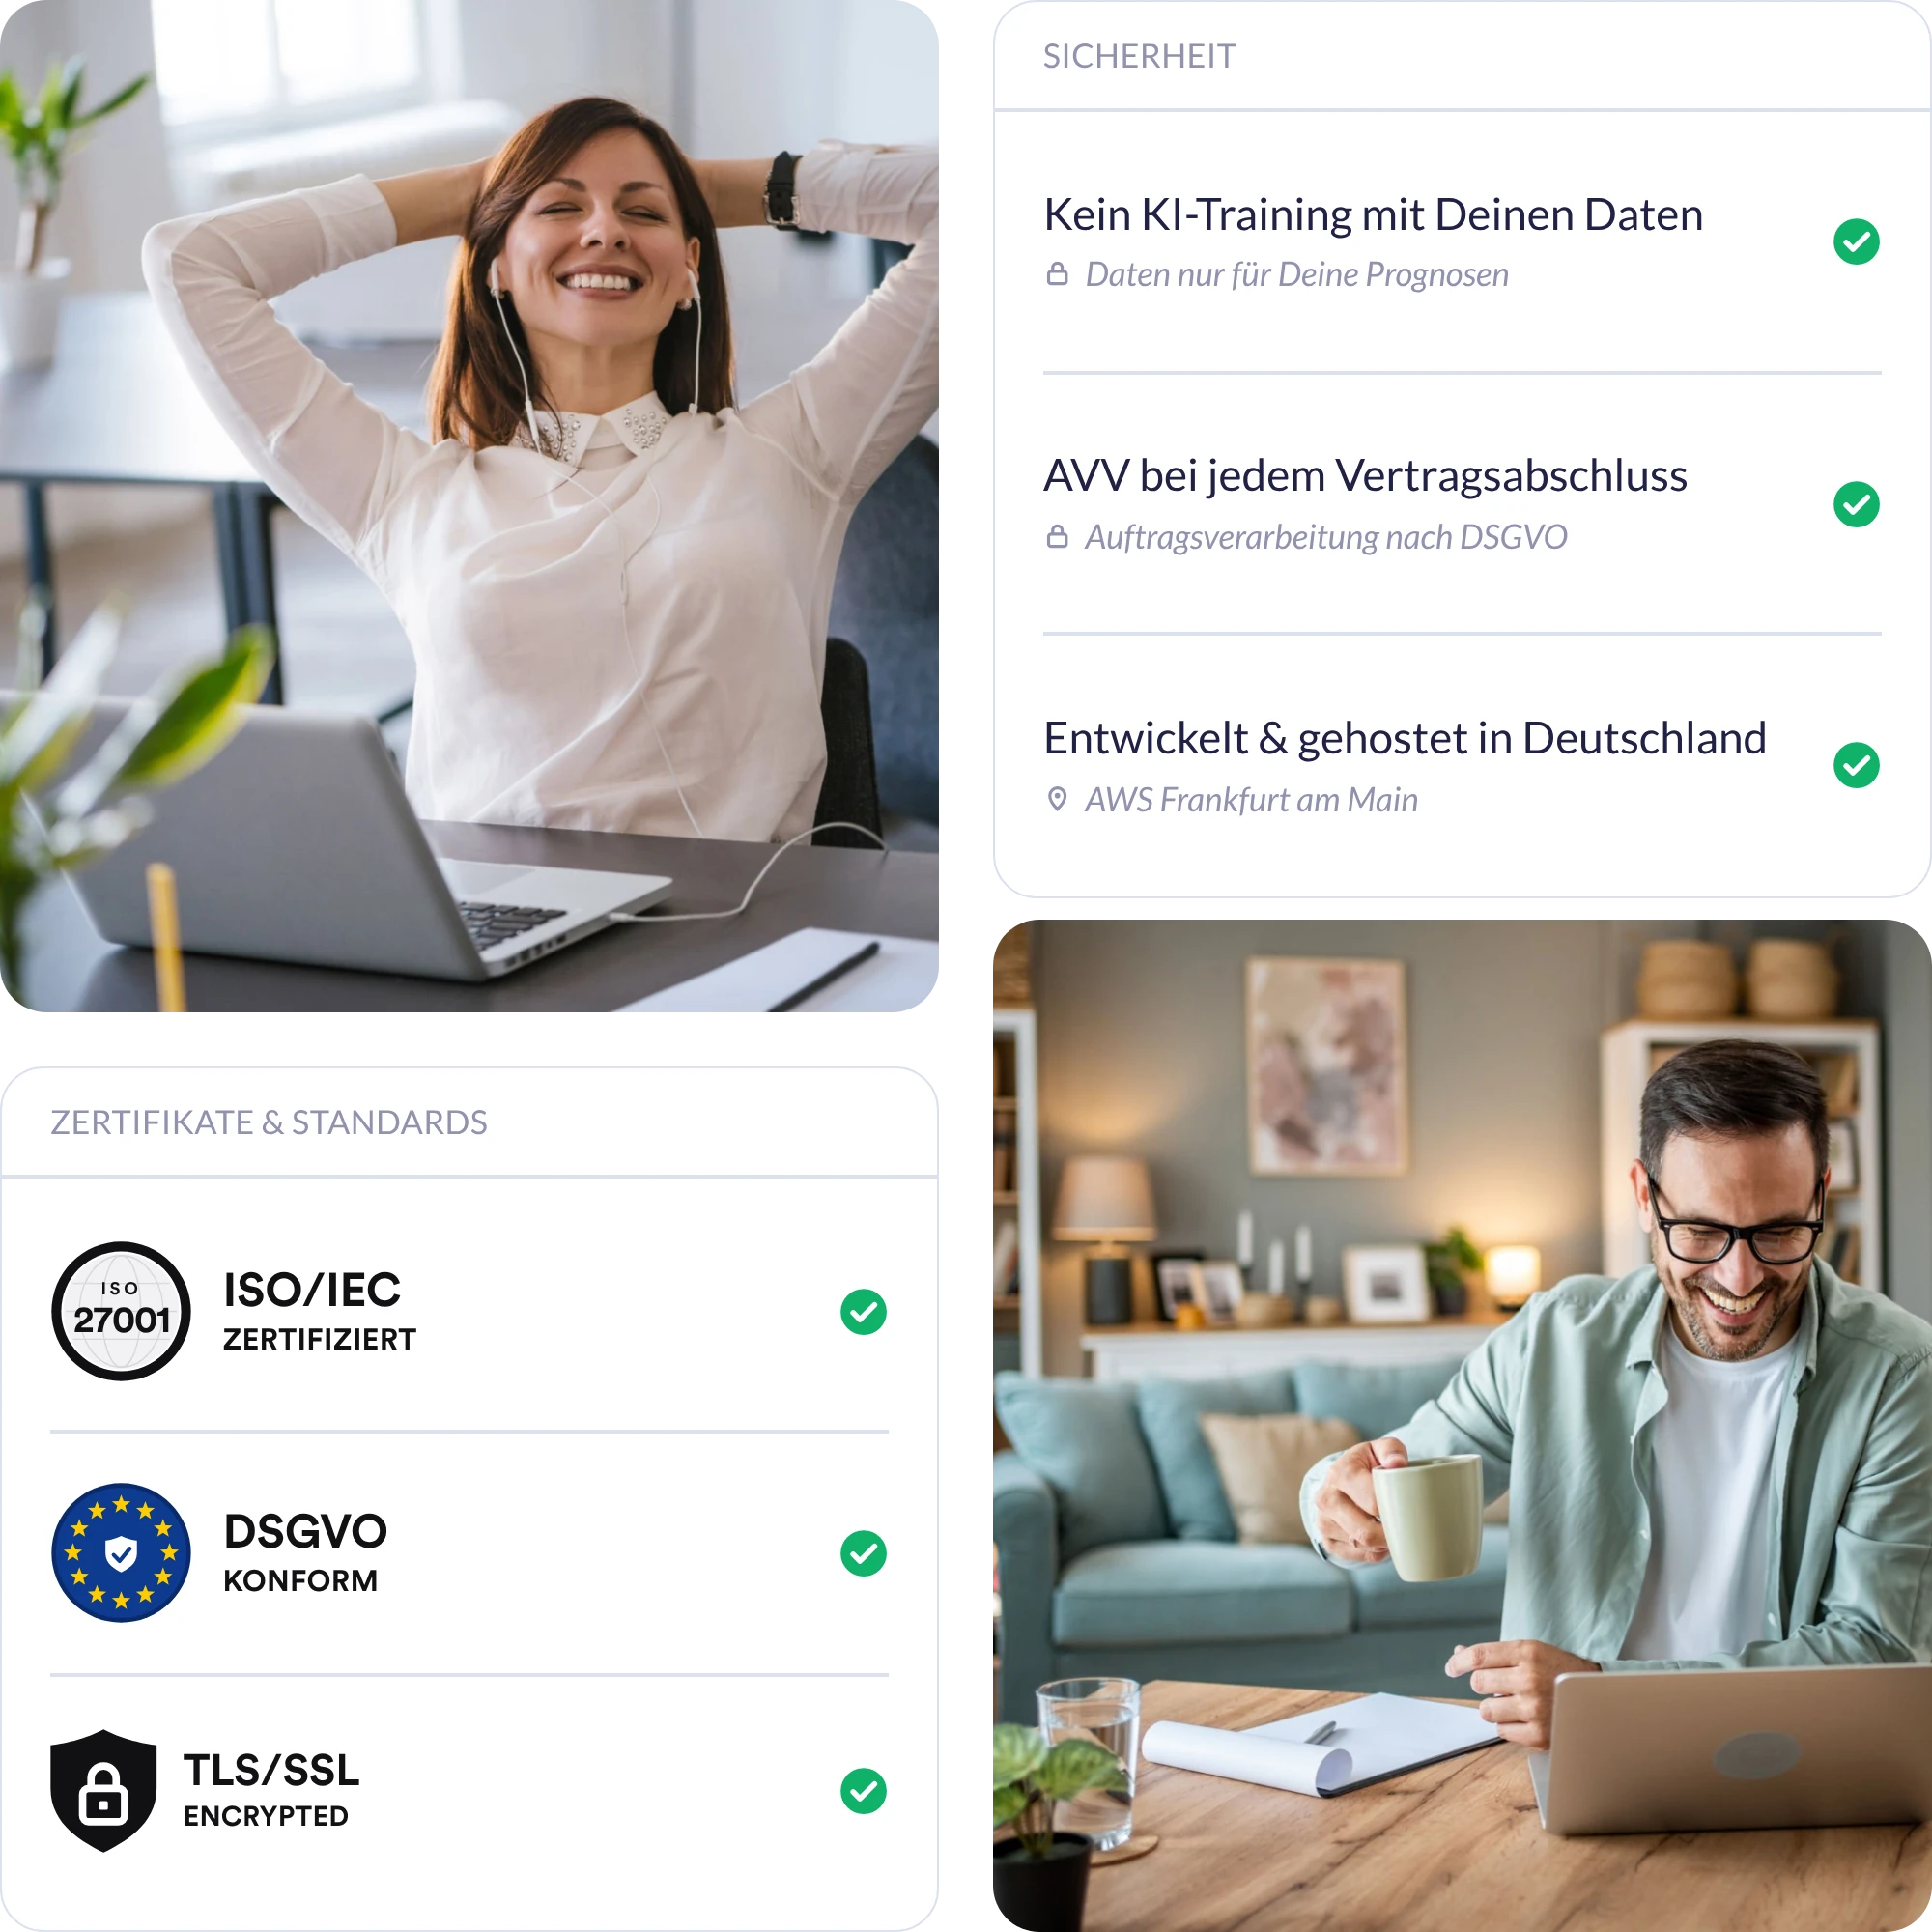
Tidely is developed in Germany and operated on servers in Frankfurt am Main. We are ISO/IEC 27001 certified and process your data in accordance with GDPR requirements. Your financial data belongs to you, and that is exactly how we treat it.




Time savings and new insights through AI.
Built on a foundation you can trust.
Tidely is developed and hosted in Germany. Your financial data never leaves German servers, is not shared with third parties, and is not used for AI training. Tidely is ISO 27001 certified and fully GDPR-compliant—so you can focus on what matters: your liquidity.
Developed and hosted in Germany
Tidely is a German company based in Munich. Your financial data is processed on German servers and is never shared with third parties.
Tidely is ISO 27001 certified
ISO 27001 is the internationally recognized standard for information security. Tidely meets these requirements.

GDPR-compliant and designed for the EU
Tidely is fully GDPR-compliant. Your financial data is processed in accordance with European data protection laws—without routing through third countries and without hidden data flows.
How we protect your financial data
Liquidity data is among a company's most sensitive information. That is why Tidely relies on verified standards: servers in Germany, GDPR-compliant data protection at the highest level, and certification according to ISO/IEC 27001, the internationally recognized standard for information security. Our AI uses your data exclusively for your own forecasts. You can find all the details in our privacy policy and the Data Processing Agreement.
ISO/IEC 27001 certified
Tidely is certified according to ISO/IEC 27001, the internationally recognized standard for information security. This standard defines how a company systematically identifies, assesses, and mitigates data risks—from access rights and technical security measures to clear procedures in emergencies. Independent auditors regularly verify compliance with these requirements. For you, this means that security is not just a promise, but a verified component of all our processes.

Developed and hosted in Germany
Tidely is a Munich-based company and is developed in Germany. Your data is stored in the AWS data center in Frankfurt am Main, with an additional backup located in the EU. This ensures your financial data is stored within the EU and is subject to European data protection law. This way, you always know where your data is and which rules apply to it.

GDPR compliant
We process your data in accordance with the General Data Protection Regulation (GDPR). Bank-level encryption protects it both during transmission and storage. With every contract, you receive a Data Processing Agreement (DPA) that bindingly regulates how we process your data on your behalf. Our privacy policy describes in detail how we handle data beyond this.

AI compliant with the EU AI Act
We use AI in accordance with the EU AI Act. It analyzes your financial data, identifies recurring income and expenses, and uses them to create liquidity forecasts. Every assumption remains transparent: you can see what a forecast is based on and adjust any plan at any time. You are always the one making the decisions—no black box.

No AI training with customer data
Your financial data is not used to train AI models. We use it exclusively to generate your own forecasts. This keeps confidential figures like revenue, account balances, or salaries exactly where they belong: in your Tidely account. Our team is happy to answer any questions regarding security and data protection at security@tidely.com.

What customers say: Tidely's impact on planning security and operational agility

As an independent Pilates studio, we face new challenges and changes every day—and not just since the pandemic. Thanks to tidely, we can focus on our fitness offerings without worrying about outstanding invoices, and we can easily ensure our long-term liquidity.


What I like about tidely is that I can get a clear overview of how our cash flow behaves under different scenarios in just a few minutes. All bank accounts can be connected and synchronized in real time.


We finally have the ability to automate our accounting processes, which saves us countless hours of work and a lot of stress! Tidely allows us to create detailed financial plans exactly the way we want them, and we are very grateful for that!


I have been creating plans for the coming year for 30 years. I have never finished so quickly, and I also believe that the plan has never aligned so accurately with the actual situation. Because I am connected to my account, I can no longer forget anything or simply leave things out.
Highly intuitive software! The user-friendly interface makes it easy for even untrained users to get up and running quickly and intuitively. This allows you to achieve initial results in no time and contribute to the company's transparency.
Tidely is a tool that gives us an up-to-date overview of our financial status. It also greatly simplifies our cash flow planning. The interface is incredibly clear and features a very innovative design. So far, the program has saved us a significant amount of time and improved our workflow.

In my view, Tidely is one of the most useful tools for e-commerce companies. Since implementing Tidely, my overall peace of mind has completely changed. Tidely gives me a great sense of security and lets me sleep soundly, simply because I know I have a clear view of all my numbers now.

Finally, no more Excel-based cash flow planning! Connecting your company accounts makes reconciling and categorizing transactions so much easier. Plus, the automated categorization based on historical transaction data saves a significant amount of time.
The ability to easily create categories and rules, the automatic synchronization of all bank accounts, and the scenario planning features all round out a straightforward and secure approach to liquidity management for our company. A standout feature, however, is the excellent customer service and support, which provides truly tailored solutions.

With Tidely, I can provide figures quickly, and that is simply invaluable! I have much better visibility into our liquidity and can justify the numbers to bank advisors and my employees at any time.


I would honestly recommend Tidely to every company. I can’t think of a single business where it wouldn’t be useful. After all, if you don’t have an overview of your liquidity, you’re flying blind—and whether you succeed or not is just down to luck.

Schedule a free consultation
In a brief call, our product experts will evaluate your requirements with you and answer your questions. After that, you can start your trial phase immediately!


Frequently asked questions about security and data protection
Here you will find the most important answers regarding data protection, data security, and the use of AI at Tidely.
Where is my data stored at Tidely?
Your data is stored in the AWS data center in Frankfurt am Main, with an additional backup located within the EU. Your financial data is therefore stored within the EU and is subject to European data protection law.
Is Tidely ISO 27001 certified?
Yes. Tidely has been certified since 2025 according to ISO/IEC 27001, the internationally recognized standard for information security. Independent auditors regularly verify that these requirements are being met.
Is Tidely GDPR compliant?
Yes. We process all data in accordance with GDPR requirements. With every contract, you receive a Data Processing Agreement (DPA) that governs how we process your data on your behalf.
How is my data encrypted?
Your data is protected with bank-level encryption, both during transmission and while in storage.
Can Tidely move money from my account?
No. Tidely only reads account transactions and balances to display and plan your liquidity. The connection to over 5,000 banks is handled via our interface partners finAPI, Salt Edge, and BANKSapi.
Does Tidely use my data to train AI?
No. Your financial data is not used to train AI models. We use it exclusively to generate your own forecasts and analyses.
How does Tidely use AI?
Tidely uses AI in compliance with the EU AI Act: for the automatic categorization of your transactions, for forecasting your liquidity, and for "Chat with your Data," which allows you to ask questions about your financial data directly in the chat. For quick support requests, a chatbot is available to answer your questions. Additionally, there is an MCP server in beta that allows you to connect Tidely with AI assistants.
Every forecast remains transparent and adjustable. You make the decisions.
Who can I contact if I have questions about security?
Our team is available to answer questions regarding security and data protection at security@tidely.com.